
That may seem like a melodramatic title, but now that we’ve got your attention: ransomware.
When a cyber-attack happens, the question of ‘why’ is usually somewhere near the bottom of the list of immediate priorities, but it is still important, and with a ransomware attack, the answer is usually relatively simple: money. When James Hall & Company was the victim of such an attack in December 2021, over 300 SPAR stores were forced to close or revert to cash-only transactions for the duration of the attack. Although the firm didn’t disclose if it had or would pay the ransom, that is not the only cost to an organisation undergoing a ransomware attack; in fact, it could end up being the smallest part of what the organisation ultimately loses.
The immediate threats of a ransomware attack are clear: there’s the ransom itself, the fact that your data is at risk of exposure, and the cost in terms of lost revenue during the downtime (depending on the number of critical servers and applications affected, a single minute of downtime can cost anywhere between $4,998 and $16,700 per server). There is, however, an even worse knock-on effect. Returning to the example of SPAR; when a convenience store has to close due to being unable to process a payment, or even if it remains open but can only process cash payments, that convenience store is no longer convenient, and that is what the lasting impression will be to the average consumer. On top of that, organisations ‘may also be liable for civil penalties stemming from their failure to meet Service Level Agreements (SLAs) or compliance regulations’[i]. In short, the brand damage that can result from a ransomware attack has the potential to be what causes the most severe long-term harm to a business.
When faced with the kind of damage that an attack like this can cause, it’s easy to see why organisations pay up. But of course, that’s a decision that no one wants to make, and even if the money is paid, recovering the encrypted data takes still more time (an average of 23 days), if it can even be recovered in its entirety – for context, an average of 65% of data is recovered using the decryption key provided by ransomware attackers, and only 8% of organisations are able to recover all of the data. Additionally, while the attacker will usually honour their promise not to publish any data if the money is paid, there’s still nothing to stop them from sharing or selling the data to other attackers, opening the organisation up the increased likelihood of more attacks.[ii]
Download the ‘Gartner Report: Quick Answer: Ransomware – What Happens If You Pay?’ to find out more about the risks of paying a ransomware attacker:
The key takeaway of this is that a ransomware attack is usually disastrous from every perspective, regardless of whether the ransom is paid. The unfortunate reality, however, is that the growing adoption of cloud and hybrid environments, coupled with the increased sophistication of contemporary cyber threats, has created an environment that traditional EDR tools alone are not equipped to manage; it becomes virtually impossible to stop malicious traffic at the network perimeter when that perimeter is constantly changing. Ransomware can very easily enter a network encrypted or disguised as something benign, spread laterally within that network and lie dormant and undetected until it receives a command from the attacker. The most effective defence against ransomware lies not in stopping it at the network perimeter, but in being able to respond quickly once the malicious traffic is inside the network, where it’s most vulnerable; what is known as defence in depth. A network detection and response (NDR) solution can give IT teams the means to do just that.
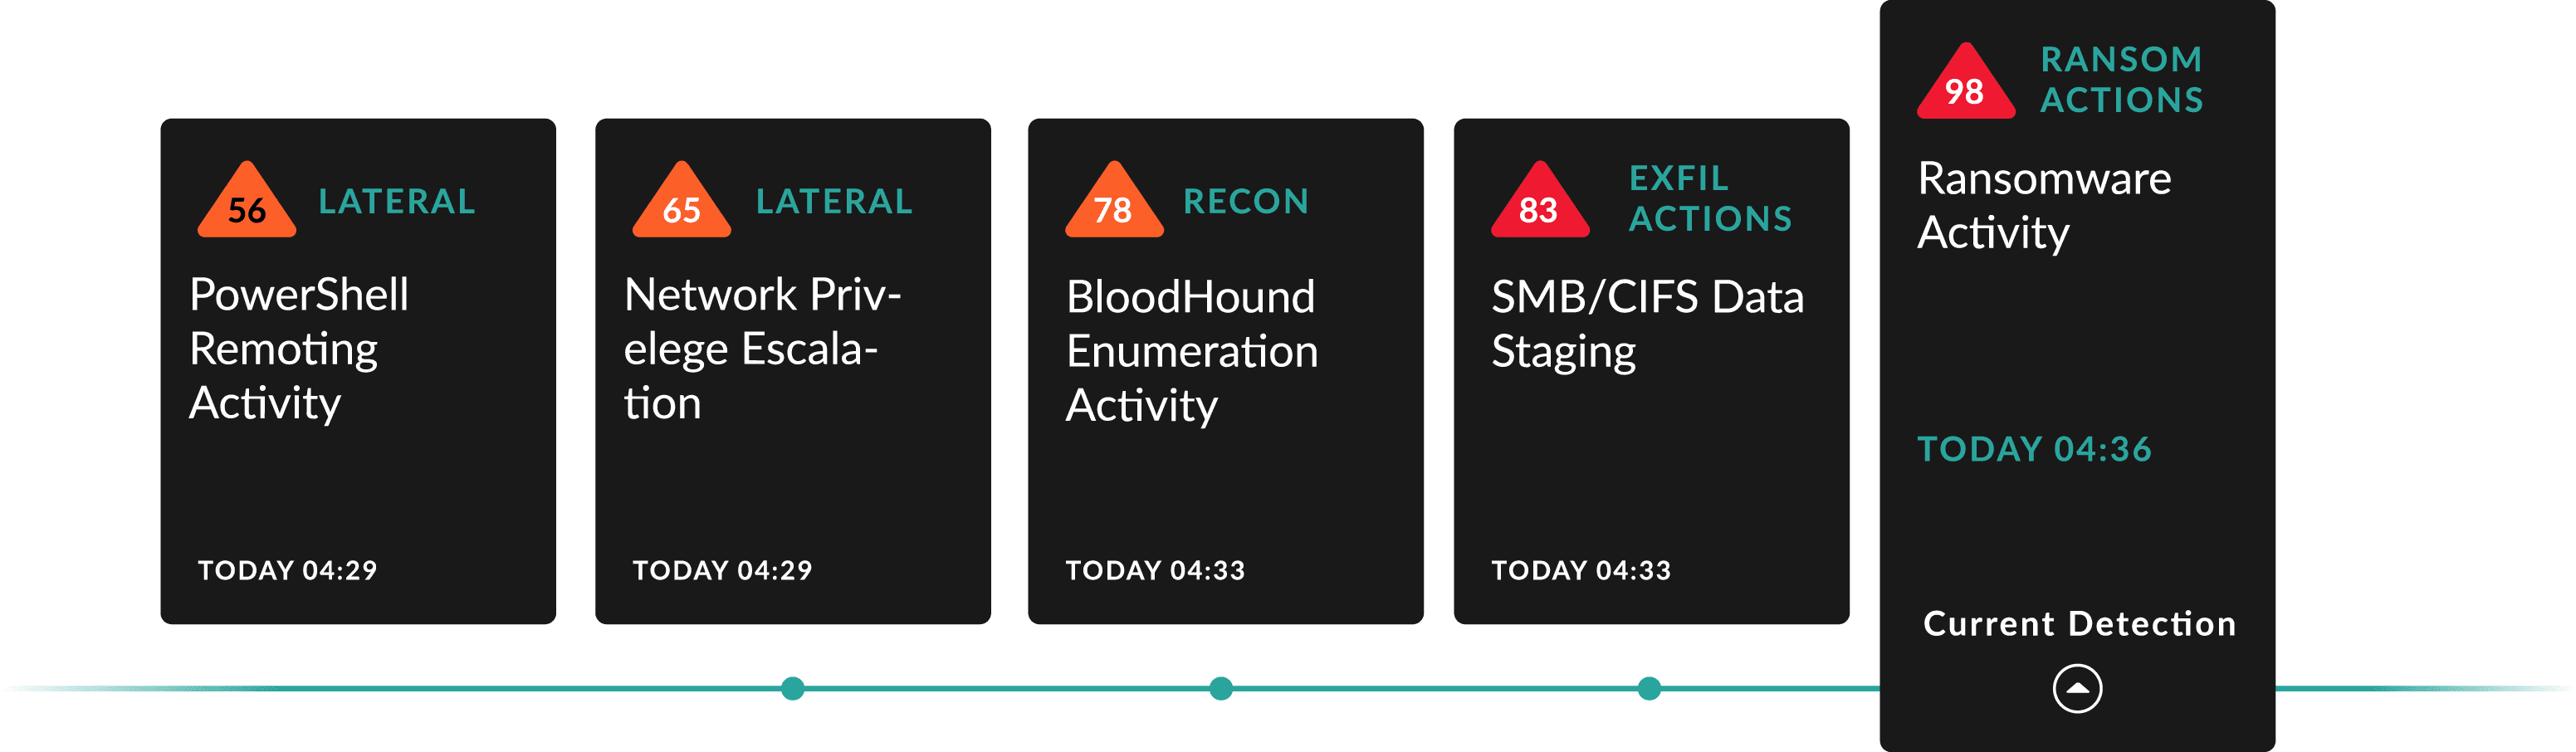
ExtraHop’s Reveal(x) 360 solution provides you with all the intel and tools you need to gain complete visibility into your network and respond to malicious activity 84% faster. It uses machine learning to enable you to detect behaviours that signal a potential ransomware attack, and get it contained before it starts.
Want to learn more about how ExtraHop can help you stop a ransomware attack before it starts? Find out more here:
Ransomware Mitigation & Detection Solution
__________________________________________________________________________________________________
References
[i] The Cost of Enterprise Downtime | TechChannel, Laura DiDio, 30 September 2021
[ii] Quick Answer: Ransomware – What Happens If You Pay?, Mark Harris, Paul Webber, Chris Silva, 5 August 2021
Other recent news

Bridging the Gap: Intune Co-Management with Hexnode

The Narrowing Race to Quantum: Insights from World Quantum Readiness Day

Lengthening Shadows: Key Lessons from the 2026 Cybercrime in the Age of AI Report

Event Round-Up: Kite Partner Golf 2026

